Management review
Prepare the ISO 27001 management review and NIS2 management body oversight with complete inputs, logged decisions and planned follow-up.
Typical requirementsISO 27001 9.3NIS2 Art. 20DORA Art. 5
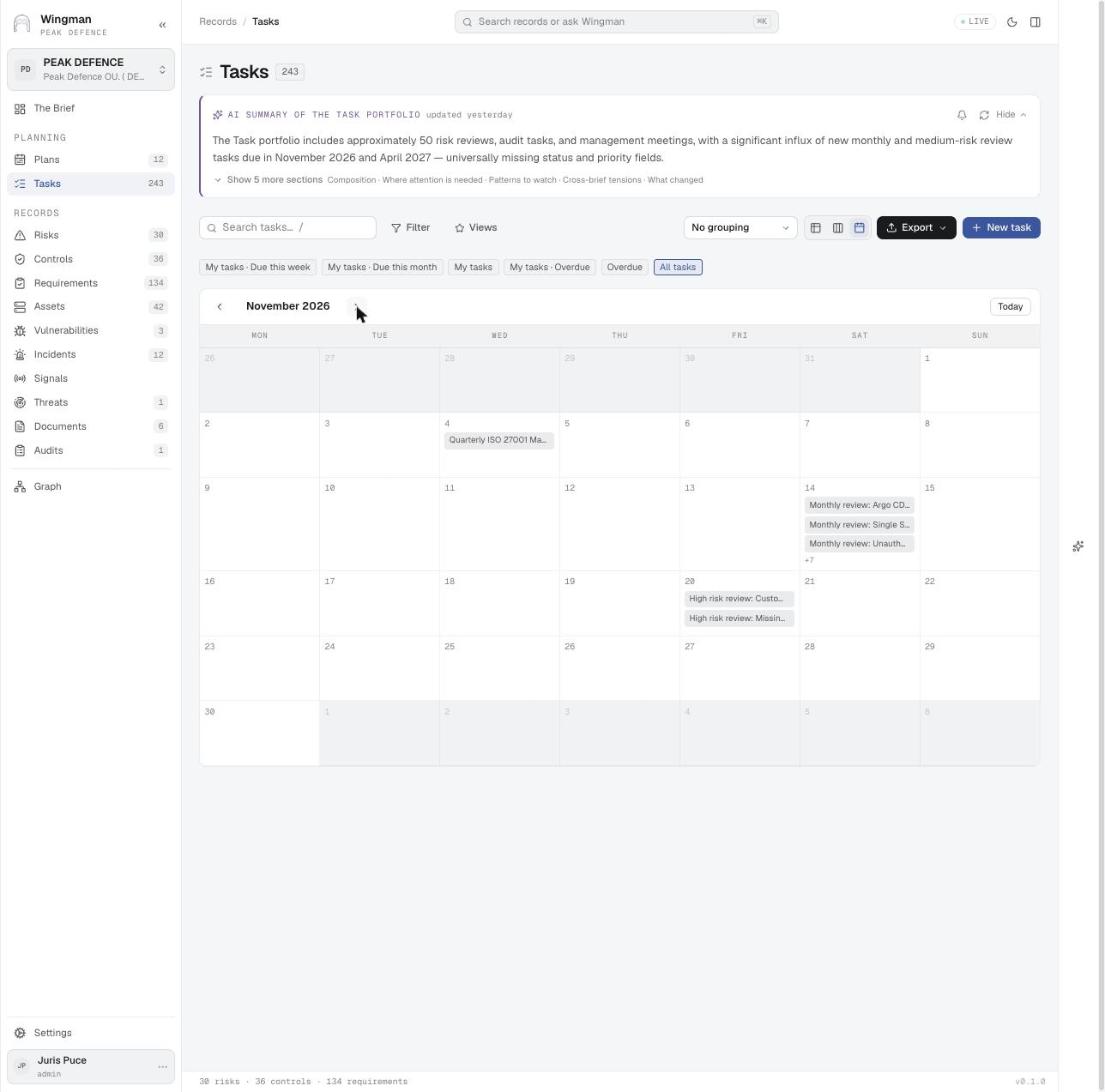
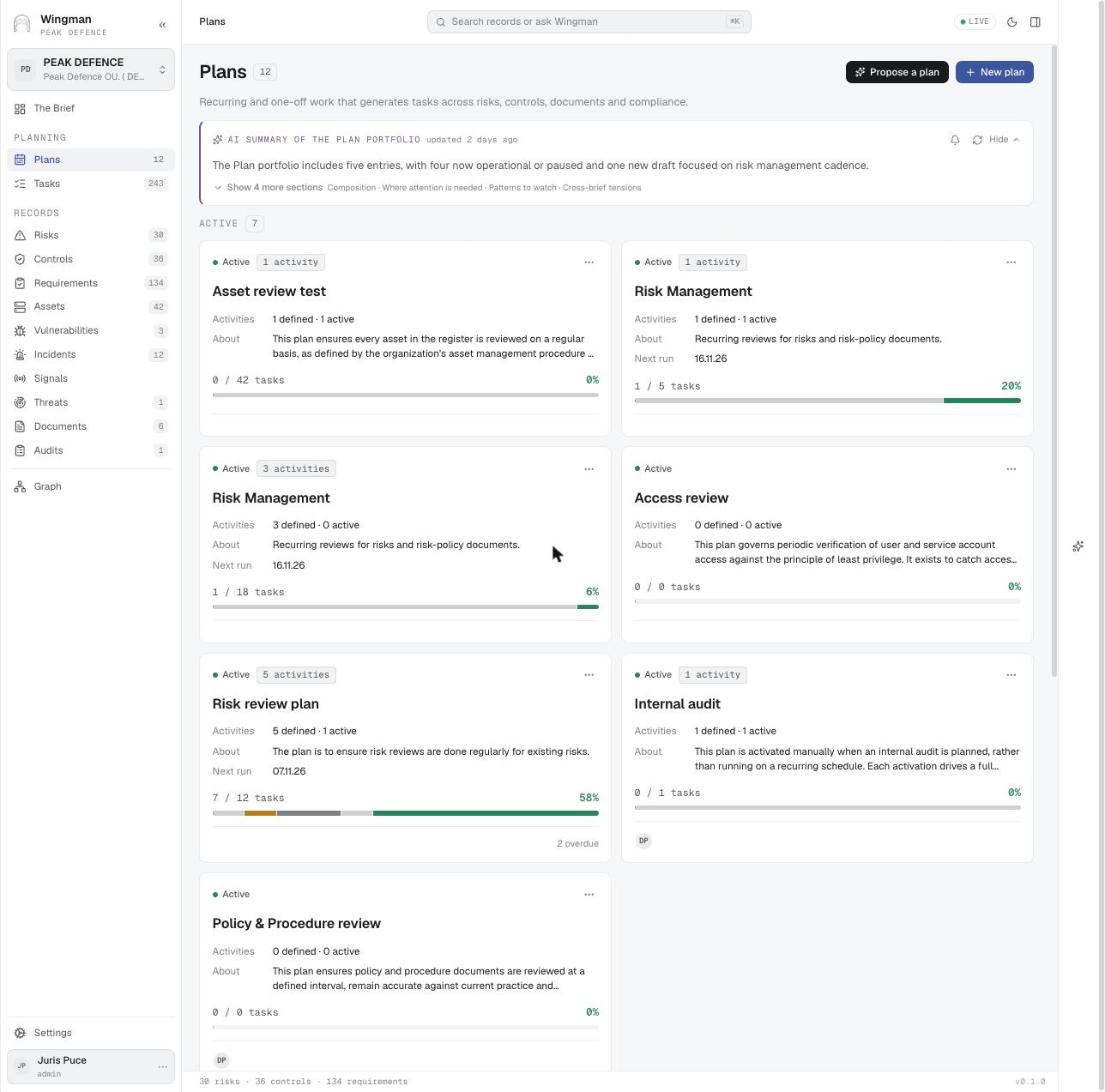
Screens for this stage · Stage 1: Schedule
Sector angles
What this use case looks like under specific regulations.
NIS2
The management body sees exposure, incidents, overdue work and approves the measures, with minutes and decisions kept.
Financial sector
The management body reviews exposure against risk appetite, events and remediation status.
ISO 27001 / SOC 2
Inputs required by clause 9.3 come from live records; decisions become tracked tasks.
Videos


Plays from youtube-nocookie.com. YouTube sets no cookies until you press play.
Other use cases
New requirements
Implement a new regulation or standard by reusing and linking what already exists, then drive the rest with tasks and plans.
GDPR and DPIA
Keep processing chains and their risks current, and support data protection impact assessments.
EU AI Act
Keep an AI use case registry and link each use case to its obligations, risks and controls.