PEAKDEFENCEWINGMAN · Use cases

Roles and RACI

Make responsibilities explicit, and find gaps in coverage and conflicts in segregation of duties.

Typical requirementsISO 27001 5.3NIS2 Art. 20DORA Art. 5

Screens for this stage · Stage 1: Roles
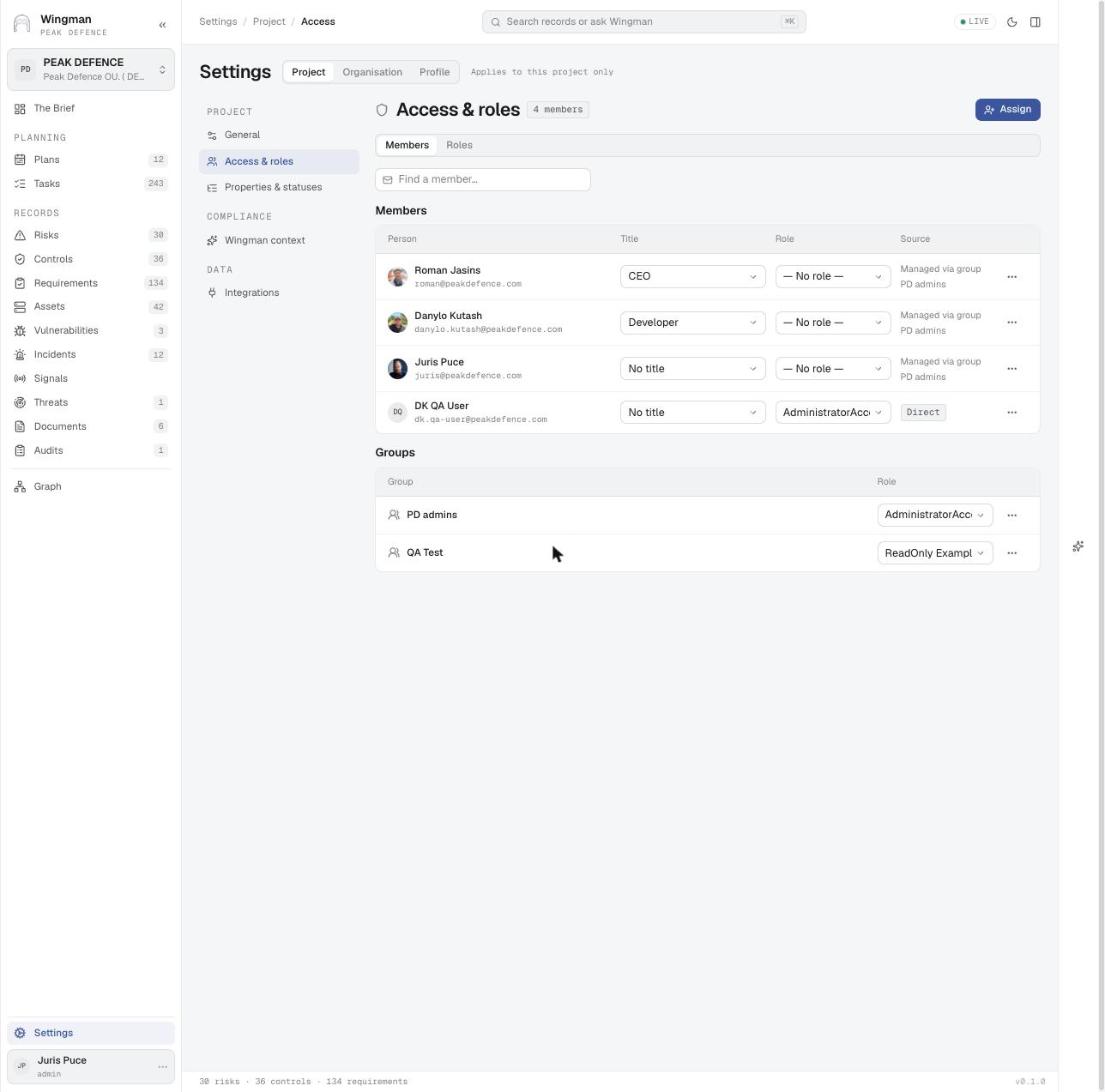
Members, titles and roles
Settings Members, titles and roles Each member has a title (CEO, Developer, Incident Response Lead, CISO) and an access role, directly or through a group.

Screens for this stage · Stage 2: RACI on every record
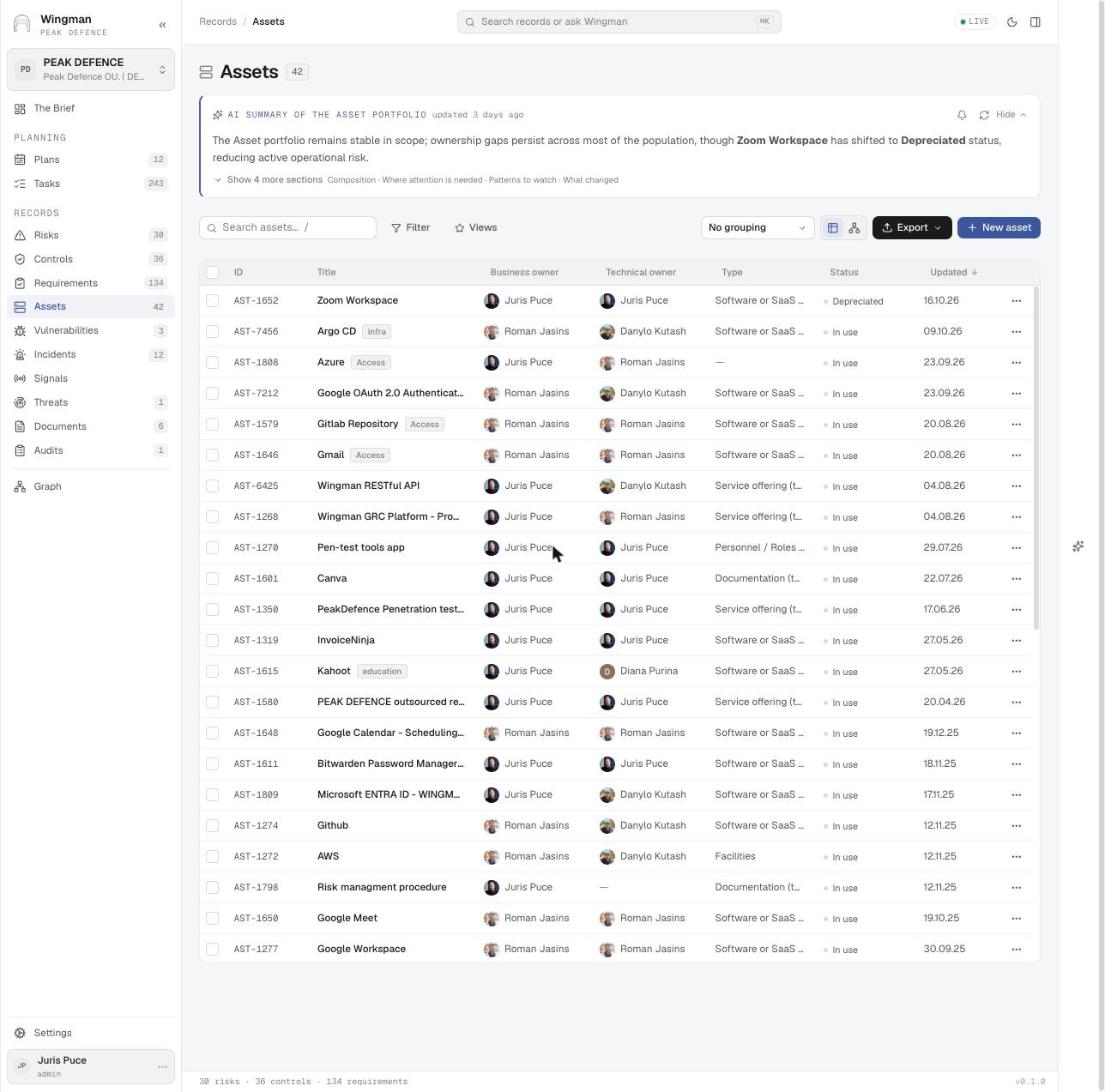
The asset registry
Assets The asset registry Business owner and technical owner per asset, type (software, service offering, documentation, facilities), status and tags. Suppliers, provided services and AI use cases are subtypes.

Screens for this stage · Stage 3: Coverage gaps
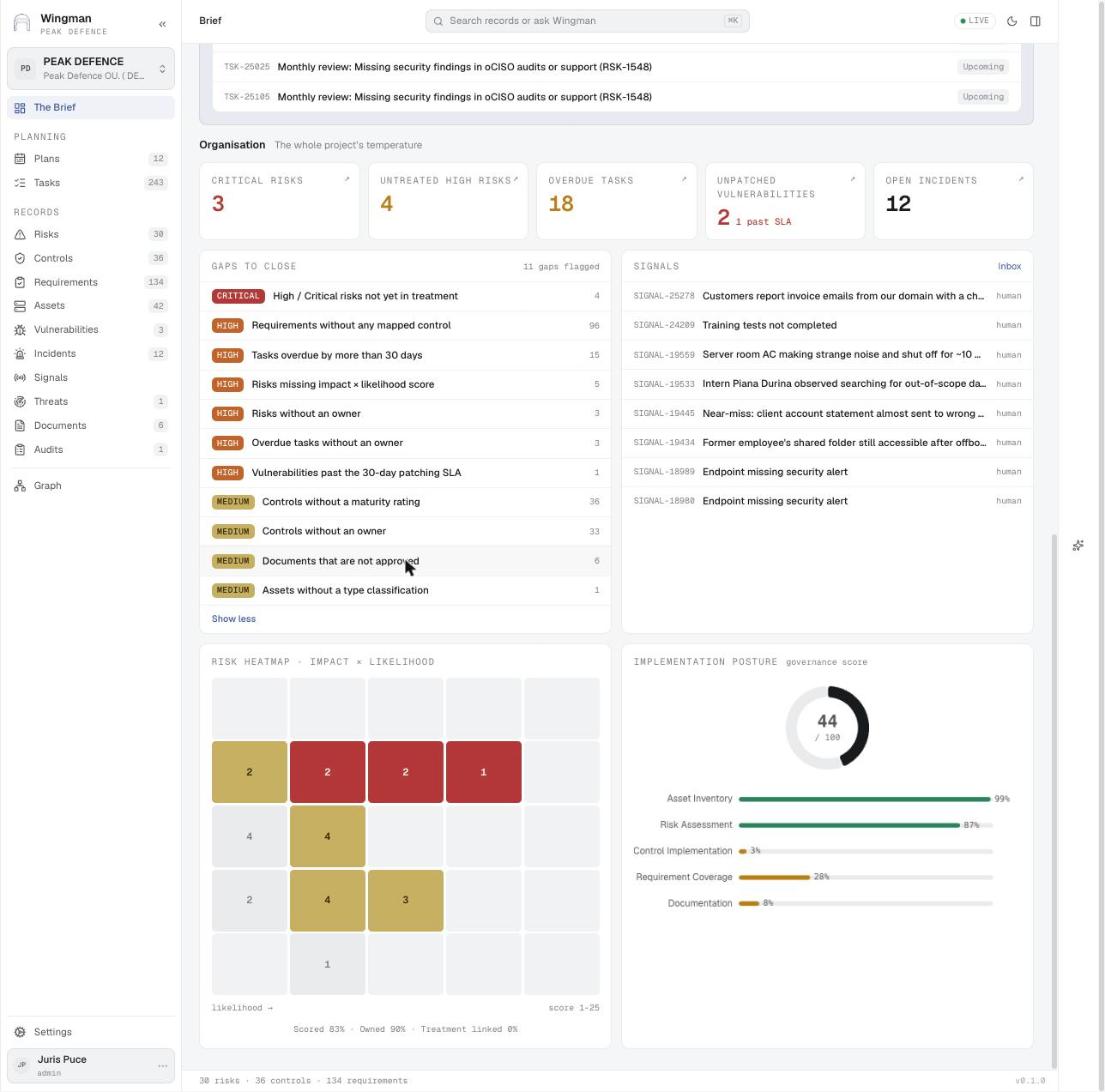
Gaps to close and the organisation's temperature
The Brief Gaps to close and the organisation's temperature Eleven register checks run on every record: risks without an owner or score, requirements without a control, tasks overdue by more than 30 days, vulnerabilities past the patching SLA, unapproved documents. Each gap links to the records behind it.
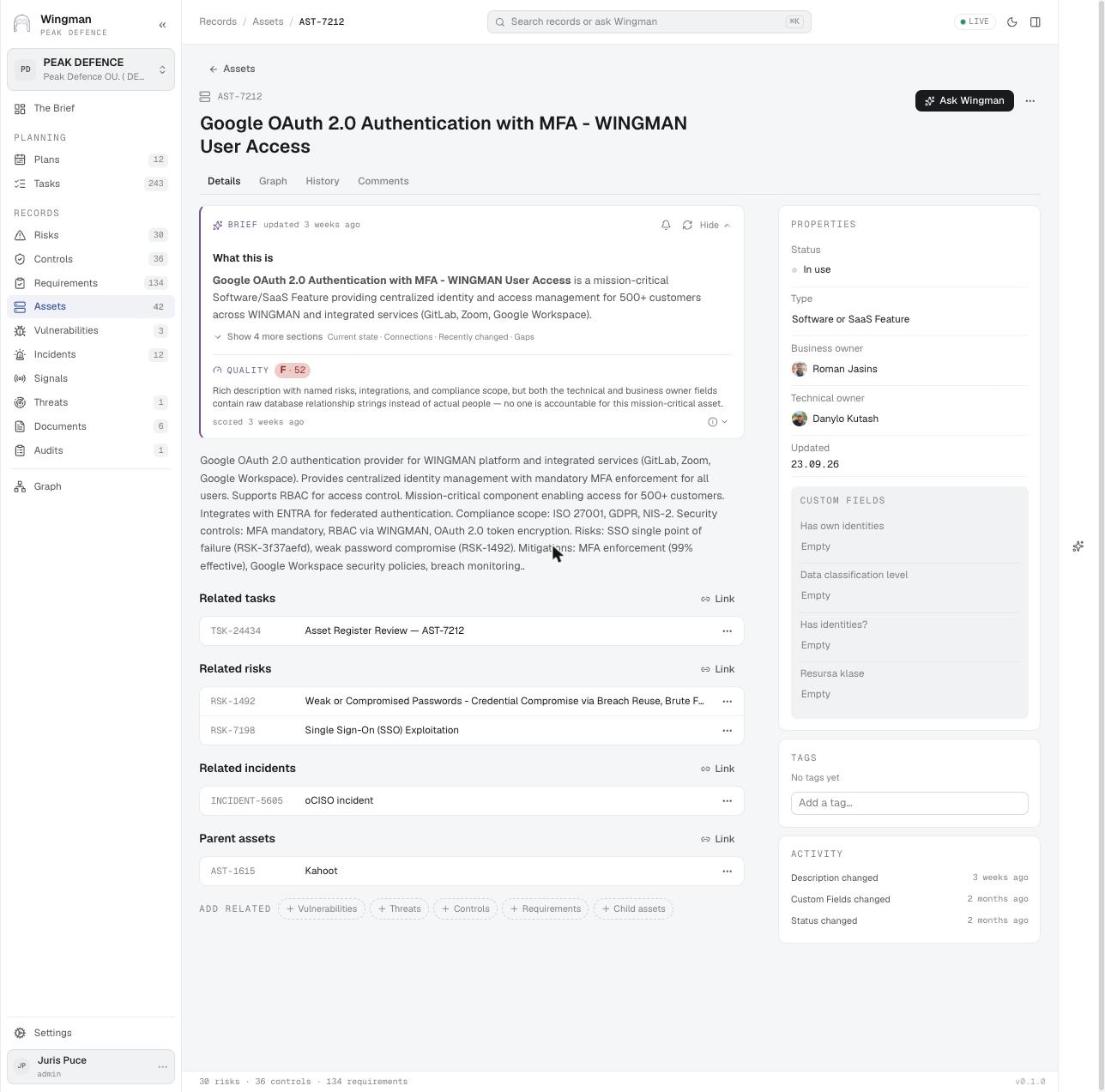
An asset with its quality score and dependencies
Assets An asset with its quality score and dependencies The identity provider for 500+ customers: a data-quality score with the reason (owners recorded as raw strings), related risks and incident, a parent asset, and custom fields for data classification.

Sector angles

What this use case looks like under specific regulations.

Videos

ISMS implementation with WINGMAN AI Building an information security management system in WINGMAN, from requirements and scope to risks, controls, owners and the review cycle.

Plays from youtube-nocookie.com. YouTube sets no cookies until you press play.

Other use cases

All use cases

See WINGMAN on your own data

We can walk through any of these use cases with your requirements, risks and controls.

Contact Peak Defence